One control loop for verified attack-path interruption.
Circuit builds an Asset Graph from the tools you already run, decides with deterministic policy, acts through your own controls with your approval — and proves the result.
Circuit is in development. This page describes the architecture we’re building and proving; the screens are from Circuit 1.0 Alpha in our lab.
Every use case runs through the same stages, each with its own component. Each stage is explicit, so you can see what Circuit knew, what it decided, who approved, what changed and how it was proven.
01
Context
Connectors
Connectors ingest the facts decisions need — identities, sessions, privileges, assets, vulnerabilities, network observations and data classification — rather than all of your raw telemetry.
02
Correlate
Asset Graph · path engine
Entities are resolved by stable identifiers, never by display name — and shown to people by name. Every relationship keeps its source system, observed time and freshness, and a path exists only when every condition is backed by evidence; observed activity stays distinct from theoretical reachability.
03
Decide
Policy & decision
Deterministic, versioned policy decides whether a path is material and what may be done about it. Unknown or stale evidence lowers confidence and is shown — it is never assumed.
04
Recommend
Intervention planner
Circuit ranks every control point that can actually break the path and recommends one — reversible where possible. Before anyone approves, any other can be used instead, or a companion added alongside; the rest stay ready if enforcement fails.
05
Approve
Approvals
The approver reviews the exact change and signs it with a FIDO2 security key. The signature is bound to that command and nothing else, and whoever asked for the change can’t approve it.
06
Enforce
Enforcement executor
An executor in your environment checks the signature, the approval and your signed policy, then applies the command through your control — endpoint, identity, cloud or network. A failure is explicit, never silent.
07
Verify
Verification
Circuit re-reads the authoritative sources and recomputes the path. It is marked broken only when fresh evidence shows it no longer resolves end to end; residual risk stays open, with an owner.
+
Evidence
Evidence ledger
Every outcome — the path, each agent run, the approval, the command, the downstream response and the verification — is sealed once and in order in a tamper-evident log in the style of RFC 6962, signed with your key and copied to your own write-once storage. The same record drafts the CERT-In report.
Circuit AI
AI that works inside the loop — never around it.
Three agents, each with its own identity, typed tools, budgets and an autonomy level set by policy. Every run — its plan, each tool call and the digest of what came back — is sealed in your evidence log. In our lab, Circuit AI calls no model: its output is scripted from the facts, and every AI output is labelled.
Read onlyS3 · L0
Investigation
Settles a path’s waiting conditions with typed, read-only queries from a catalogue — checked against the connector’s allowlist and arguments at every call, within a budget per run and per hour. The records it reads go through the same normaliser rules; it never writes a relationship or a verdict.
A person decidesS2 · L1
Decision brief
Compares the control points with a what-if for each, the guardrails, open alerts and history, and recommends one with reasons, a counter-argument and citations. Its digest is bound into the approval request, so the approver signs over the brief they read.
From records onlyS1 · L0
Executive summary
What was at risk, what was done and what remains — written from Circuit’s read models, never from a source directly. Figures first, one time axis, at most two sentences, every figure cited.
Circuit 1.0 Alpha · lab demo · fictional company
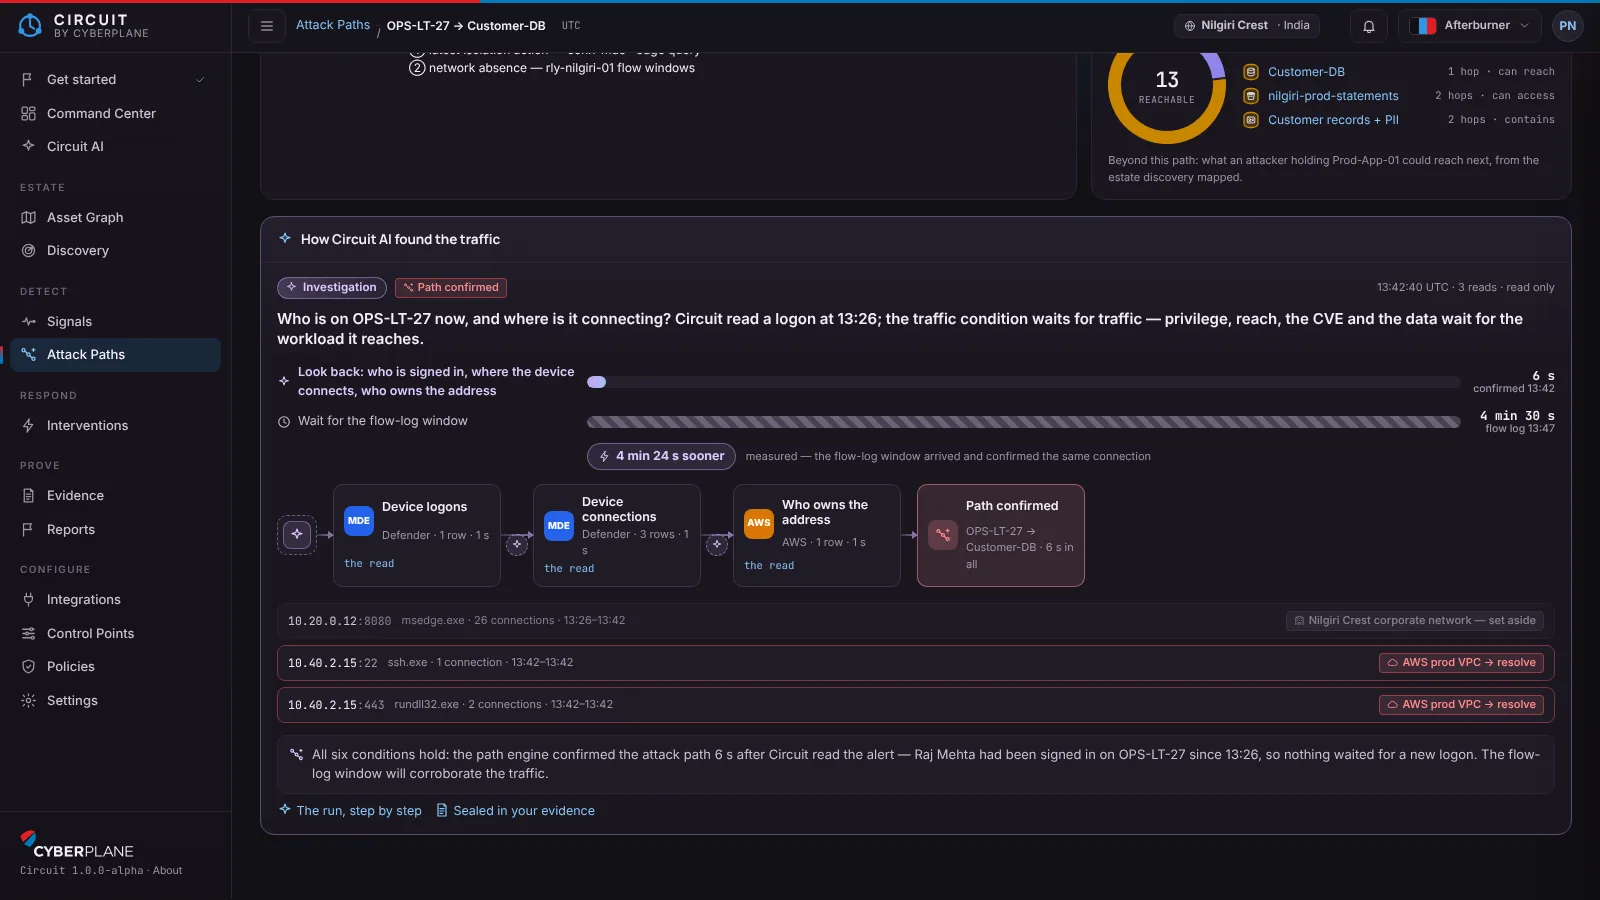
How Circuit AI found the traffic. On the attack path in our lab: Defender’s alert names a laptop someone is already signed in on, so the agent looks back — Defender for the logons and the device’s connections, AWS for the owner of each address. Three typed reads: the path is confirmed 6 s after Circuit read the alert, and the flow log confirms the same connection 4 min 24 s later.
L0
ExplainSummarise and explain — the investigation (reads only) and the executive summary
On
L1
RecommendRecommend with reasons and citations; a person decides — the decision brief
On
L2
Act with approvalPrepare the signed command; a person approves with a security key — every intervention in our lab
On
L3
Act within policyAct without a person, only for action classes you pre-approve
Not offered
L4
UnboundedAutonomy without limits
Never
Architecture
Layered by design. Composable by default.
Clear layers separate what Circuit knows, what it decides, what it does and what it can prove — so each layer can be secured, scaled and replaced on its own. The parts that can change your environment run in your environment.
Circuit cloud— operated by Cyberplane, in a regional cell
ExperiencePeople and systems
Console
Approval inbox
CERT-In report drafts
REST APIs (OpenAPI)
Evidence export
Trust & accessZero trust at every request
SSO with your identity provider
Per-request authorization
FIDO2 signing
Separation of duties
Tenant isolation
Circuit coreContext → decision → proof
Asset Graph
Path engine
Policy & decision
Intervention planner
Verification
Evidence ledger
Integration meshFacts and actions as events
Read-only connectors
Normalization (OCSF)
Event backbone (CloudEvents)
Command dispatch (OpenC2)
Outbound-only, mutually authenticated link · signed commands only
Your environment— runs in your account, under your control
Customer edgeActs on your behalf
Enforcement executor
Edge relay
Tool gateway for AI agents (planned)
Trust anchorsStay with you
Your signing keys
Write-once evidence copy
Separate read and act roles
Least-privilege calls with your credentials
Your controls— read by connectors, changed only by your executor
Endpoint (EDR)
Identity provider
Cloud IAM
Network & firewall
Vulnerability
Data classification
Architecture principles
Built the way modern security should be.
Circuit is designed as a cybersecurity mesh: composable, distributed and coordinated through shared context, policy and identity.
Cybersecurity mesh
Composable controls coordinated through shared context, policy and identity. Circuit is the coordination layer; your tools remain the controls.
CSMA concept
Zero trust
Designed so every request is authenticated and authorized — between people and services, between services, and between our cloud and your environment.
NIST SP 800-207 principles
Event-driven
Facts, decisions, commands and results flow as events, so a path is recomputed as soon as a supporting fact changes.
CloudEvents
Layered
Context, decision, enforcement and evidence are separate layers with separate privileges, so the cloud that decides can’t act on your environment by itself.
Separation of duties
Policy as code
Materiality, permitted actions and approval rules are versioned and tested like software. AI can explain a decision; it never makes one alone.
Deterministic, tested policy
Open standards
Open formats at every seam, so Circuit fits your stack and your data stays portable.
OCSF · OpenC2 · CloudEvents · OpenAPI · FIDO2
Trust model
Assume breach — even of us.
Circuit is designed so that a compromise of Cyberplane’s cloud alone can’t change your environment: the executor in your account holds the write credentials and acts only on commands signed by your approvers or allowed by a policy you signed.
Your executor, your credentials
Write credentials stay in your environment. The executor runs in your account; our cloud never holds write credentials for your controls.
Command-bound approvals
Each approval signs one exact command with a hardware-backed key. Change the command and the signature no longer verifies.
Whoever asks never approves
The person who asks for a change can’t approve it. Approvers come from a roster your admins signed, and your executor checks every approval against it before it acts.
Separate read and act paths
Discovery uses read-only access. A distinct, least-privilege identity performs only the actions your policy permits.
Evidence signed with your key
The record is append-only and its integrity can be checked outside Circuit, with a write-once copy in storage you control.
Only the context decisions need
Circuit is designed to ingest decision-relevant facts rather than centralize your raw telemetry. Raw data such as flow logs can stay with you.
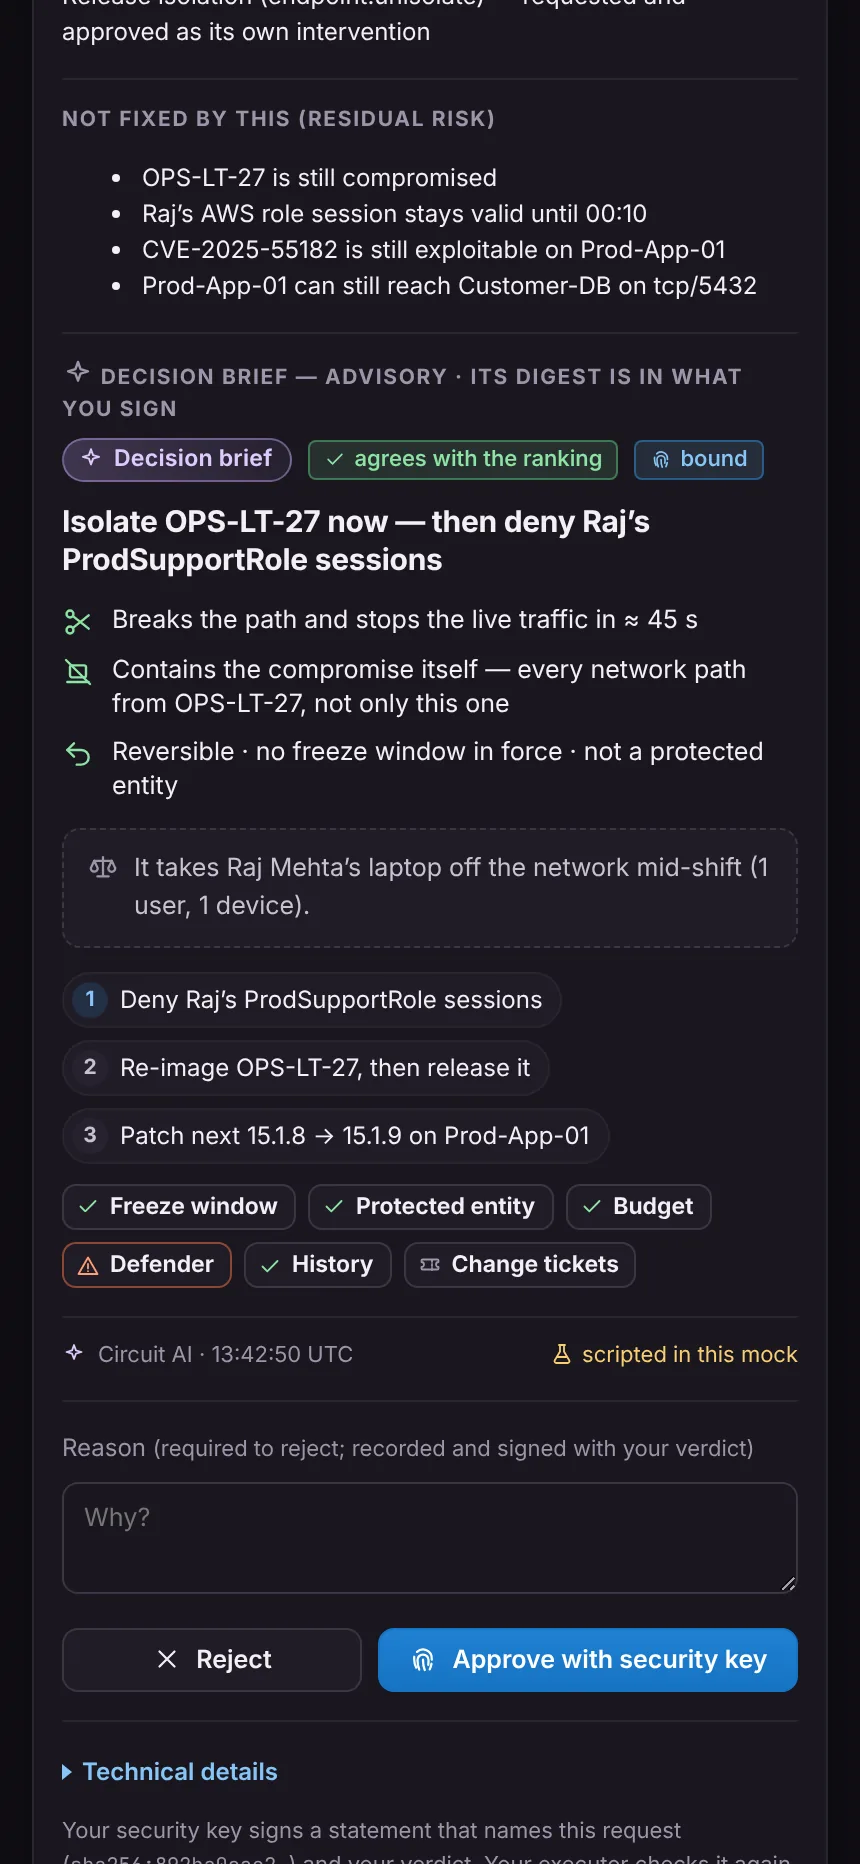
On the approver’s phone · lab demo
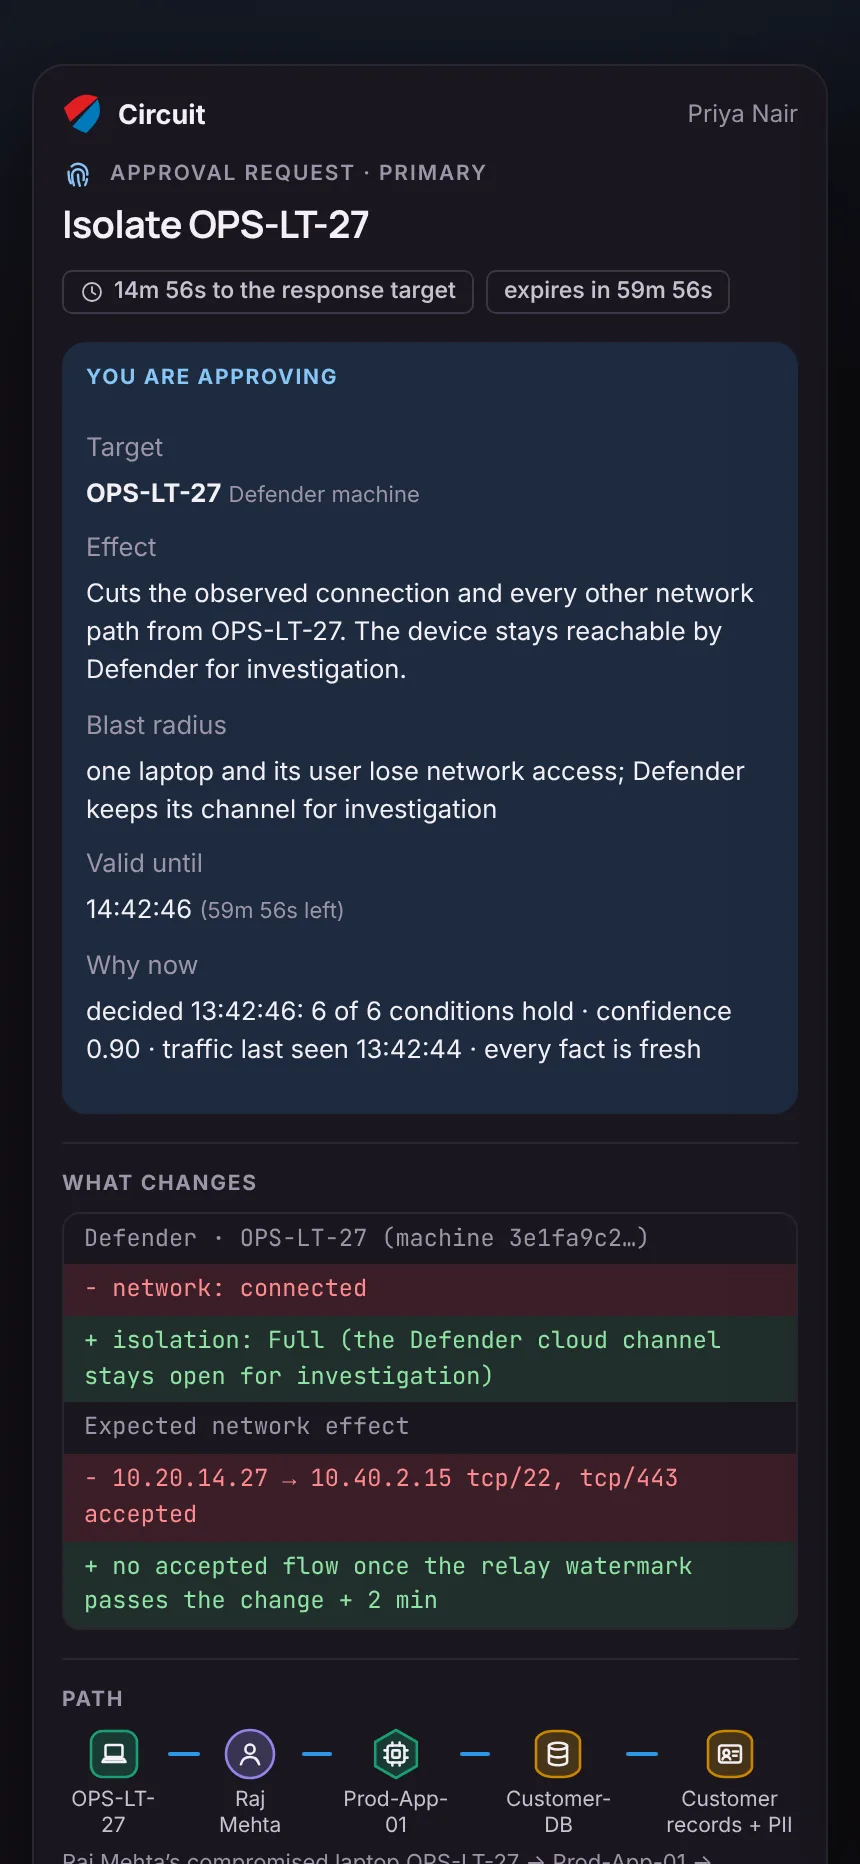
Your approver signs the exact change — and the brief they read.
The exact command. Target, effect, blast radius, how long it is valid, and the evidence for acting now.
The decision brief. The recommended cut, its reasons and a counter-argument — labelled as AI.
A security key. The signature names this one request and binds the brief’s digest.
Your executor checks again against your signed roster before it acts.
Connectors
One contract for every control.
Every connector implements the same six operations, so adding a control means writing an adapter — not new architecture. The aim: new use cases arrive as entities, policies and connectors.
ConnectAuthenticate with least privilege.
TestProve scopes and health before use.
DiscoverFind the entities and capabilities present.
IngestNormalize facts into the common model.
ExecuteApply a signed, permitted action — through your executor.
VerifyRe-read the result at the source.
First integrations, in development:
Microsoft Defender for Endpoint
Microsoft Entra ID
AWS (IAM, inventory, network ACLs, VPC Flow Logs)
CISA KEV catalog
Deployment & data
Your data where it belongs.
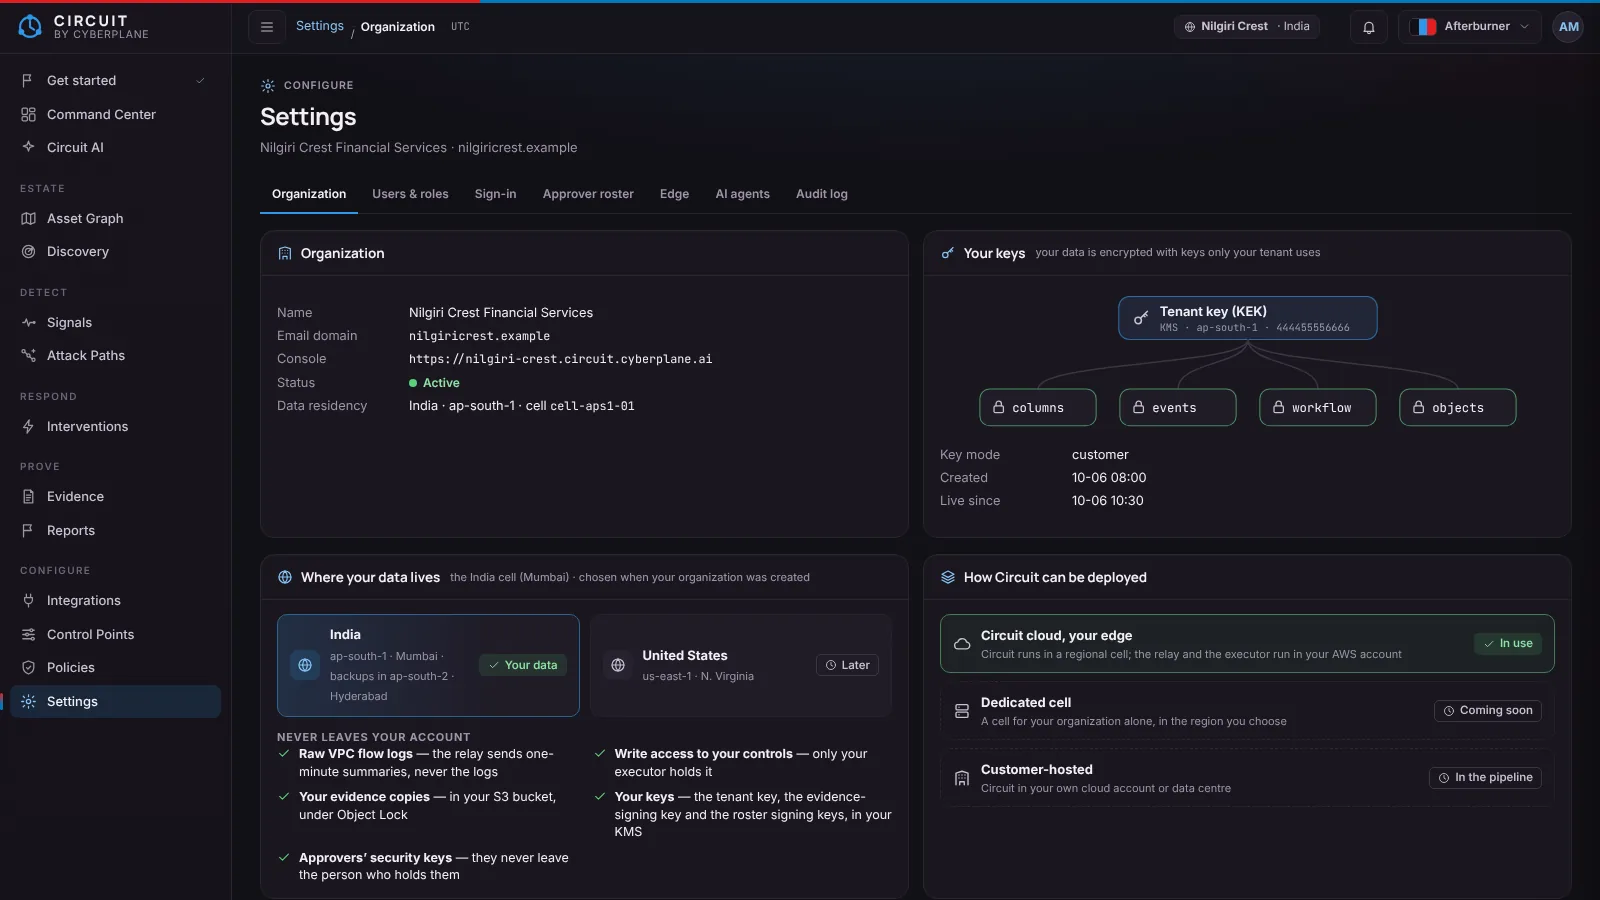
Circuit is designed to run in regional cells, India first. In our lab it runs as a Cyberplane-operated cell with a lightweight edge in your own cloud account; every model keeps write credentials, signing keys and your evidence copy with you.
In our lab today
Circuit cloud with your edge
Circuit runs in a regional cell — in the lab, the India cell in AWS Mumbai, with backups in Hyderabad. A lightweight edge in your account runs the executor and the relay.
You run only the edge
The edge connects out — no inbound ports
Other regions planned
Planned
Dedicated cell
A cell for your organization alone, in the region you choose, built from the same infrastructure modules.
Separate database and keys for your tenant
Private connectivity, such as private link
Operated by Cyberplane
Later
Customer-hosted
Circuit in your own cloud account or data centre, operated by your team.
The same modules, your infrastructure
For the strictest residency needs
What stays in your account.
Whichever model you use, these never leave it — in the lab and by design.
Raw VPC flow logs — your edge relay sends one-minute summaries
Write access to your controls — only your executor holds it
Your evidence copies — in your bucket, under Object Lock
Your keys — tenant, evidence-signing and roster-signing keys, in your KMS
Your approvers’ security keys
Circuit 1.0 Alpha · lab demo · fictional company
Where your data lives. Settings → Organization in the lab: India, AWS Mumbai with backups in Hyderabad — and the deployment options.
FAQ
Questions security teams ask us.
Can we use Circuit today?
Circuit is in development. Circuit 1.0 Alpha runs the full loop — from context to verified interruption — in our lab, with fictional data, and we’re inviting design partners to shape what comes next. If you’d like to be one, talk to us.
Why should we trust Circuit to take actions?
At first, you don’t have to. Circuit starts with recommendations and human approval. Automation expands only to actions your policy explicitly permits — bounded and preferably reversible — and every action keeps its evidence, authorization, execution status and verification.
What if Circuit recommends the wrong action?
You choose. Circuit ranks every control point that can break the path and recommends one; before anyone approves, any other can be used instead, or added alongside. High-impact actions stay approval-gated, whoever asks never approves, reversible actions are preferred, enforcement failures are explicit, and rollback is supported wherever the downstream control allows it.
What if the API says “success” but the exposure is still there?
Then it isn’t a success. Execution and verification are separate stages: Circuit re-reads the relevant state and recomputes the path. An intervention succeeds only when fresh evidence confirms the intended change.
Does Circuit report incidents to CERT-In for us?
No — it drafts, you submit. When an attack path is confirmed, Circuit drafts the report CERT-In’s Directions ask for from its sealed records, runs the 6-hour clock from the confirmed path (or from the first alert, if your admin prefers the stricter start), shows CERT-In’s four 6-hour tests as Circuit reads CERT-In’s guidance — for your counsel to confirm — and asks what only you can answer, such as whether personal data was accessed. Circuit never contacts CERT-In; marking the report submitted seals the time and the reference.
Where does our data live?
In our lab, Circuit runs in its India cell — AWS Mumbai, with backups in Hyderabad — and the tenant’s data stays in India; other regions are planned. Raw flow logs, write access to your controls, your evidence copies, your keys and your approvers’ security keys stay in your own account.
Is Circuit a SOAR, CTEM or BAS tool?
No. SOAR runs predefined workflows after an alert or case exists, CTEM tools discover, prioritize and validate exposure, and BAS simulates attacks. Circuit serves the mobilization stage of a CTEM program: it decides whether intervention is warranted, acts through a permitted control and verifies the result. It uses their findings as context, and SOAR can be one way it acts.
Does Circuit need all of our telemetry?
No. Circuit is designed to ingest the context its decisions need instead of centralizing your raw telemetry, which keeps cost, exposure and noise down. Raw data such as flow logs can stay in your environment.
Where does AI fit in?
Circuit AI has three agents. The investigation agent asks your tools typed, read-only questions to settle what a path is waiting for; the decision brief recommends a cut with reasons, a counter-argument and citations, and a person decides; the executive summary explains what happened from Circuit’s own records. Whether a path exists is decided by the path spec, actions are decided by policy and approved by people, agents have no write access, and every run is sealed as evidence. In our lab, Circuit AI calls no model: its output is scripted from the facts, and every AI output is labelled.
See the loop on a path that matters to you.
Bring an exposure you care about. We’ll walk you through how Circuit is designed to prove it, break it and prove it’s broken.